
自動目錄
此次主要根據[1]的文章進行letsencrypt設置,原文可能因為版本的問題?設置上略有不同,完全照抄會無法運作,經過修改後筆記下來。
系統
Rocky Linux release 9.4 (Blue Onyx)
# docker -v
Docker version 26.1.3, build b72abbb
Docker Compose
# vi docker-compose.yml
nginx:
image: nginx:latest
container_name: nginx
ports:
- "80:80"
- "443:443"
volumes:
- ./nginx:/etc/nginx/conf.d/:ro
- ./certbot/www/:/var/www/certbot/:ro
- ./certbot/conf/:/etc/nginx/ssl:ro
restart: always
certbot:
image: certbot/certbot:latest
container_name: certbot
restart: no
volumes:
- ./certbot/www/:/var/www/certbot/:rw
- ./certbot/conf/:/etc/letsencrypt/:rw
別急著啟動 docker,先完成下面的nginx設置
NGINX 設置
virtual.conf 的內容:
listen 80;
listen [::]:80;
server_name example.com;
charset UTF-8;
location /.well-known/acme-challenge/ {
root /var/www/certbot/;
}
}
上面的設定是為了確保第一次 certbot能取到 .
整個目錄的架構是這樣的:
└── nginx
└── virtual.conf
上面預先建立 nginx的目錄,並建立 virtural.conf
這段 Nginx 設定就是專門給 Let's Encrypt / Certbot 的 HTTP-01 驗證使用的,而且如果你想自己控制 Nginx 設定,推薦這種webroot方式,也就是告訴 certbot 去哪裡取得你有控制網站的證明(你是網站管理者)。
啟動 nginx 和 certbot
啟動你的 nginx
# docker compose up -d nginx
此時的目錄是這樣的:
├── certbot
│ ├── conf
│ └── www
└── nginx
└── virtual.conf
測試啟動 certbot 認證
# docker compose run --rm certbot certonly --webroot --webroot-path /var/www/certbot/ --dry-run -d [your.domain.name]
例如:
# docker compose run --rm certbot certonly --webroot --webroot-path /var/www/certbot/ --dry-run -d n.sfs.tw
Container rag-certbot-run-37a...b0 Creating
Container rag-certbot-run-37a...b0 Created
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Enter email address or hit Enter to skip.
(Enter 'c' to cancel): user@n.sfs.tw
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at:
https://letsencrypt.org/documents/LE-SA-v1.8-July-06-2026.pdf
You must agree in order to register with the ACME server. Do you agree?
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: y
Account registered.
Simulating a certificate request for n.sfs.tw
The dry run was successful.
執行時會要求你輸入eamil(非必要)及閱讀條款(按Y)
一切ok後,拿掉 --dry-run 再執行一次:
# docker compose run --rm certbot certonly --webroot --webroot-path /var/www/certbot/ -d [your.domain.name]
執行時會要求你輸入eamil(非必要)及閱讀條款(按Y)、是否分享email給EFF?(y/n)
當你的第一張憑證成功簽發後,你是否願意把你的 Email 地址分享給 Electronic Frontier Foundation(EFF,電子前哨基金會)?
EFF 是 Let's Encrypt 專案的創始合作夥伴之一,也是開發 Certbot 的非營利組織。
建立完畢後會自動在目錄中產生憑證公私鑰,certbot目錄大概像這樣,以下的內容都會自動產生,你不必手動建立。
├── conf
│ ├── accounts
│ │ ├── acme-staging-v02.api.letsencrypt.org
│ │ │ └── directory
│ │ │ └── ba16f4b9a2cc1973c20a6c299c2f2e47
│ │ │ ├── meta.json
│ │ │ ├── private_key.json
│ │ │ └── regr.json
│ │ └── acme-v02.api.letsencrypt.org
│ │ └── directory
│ │ └── af0e69ef49234e19b730f171df485212
│ │ ├── meta.json
│ │ ├── private_key.json
│ │ └── regr.json
│ ├── archive
│ │ └── your.domain.name
│ │ ├── cert1.pem
│ │ ├── cert2.pem
│ │ ├── chain1.pem
│ │ ├── chain2.pem
│ │ ├── fullchain1.pem
│ │ ├── fullchain2.pem
│ │ ├── privkey1.pem
│ │ └── privkey2.pem
│ ├── live
│ │ ├── your.domain.name
│ │ │ ├── cert.pem -> ../../archive/your.domain.name/cert2.pem
│ │ │ ├── chain.pem -> ../../archive/your.domain.name/chain2.pem
│ │ │ ├── fullchain.pem -> ../../archive/your.domain.name/fullchain2.pem <== 全鍊結
│ │ │ ├── privkey.pem -> ../../archive/your.domain.name/privkey2.pem <== 私鑰
│ │ │ └── README
│ │ └── README
│ ├── renewal
│ │ └── your.domain.name.conf
│ └── renewal-hooks
│ ├── deploy
│ ├── post
│ └── pre
└── www
└── .well-known
└── acme-challenge
├── jqg-9mj9NtpQzfzJcUa1Fy5UMy3_5YFLuaQ-gAOzNGU
└── yGpYbhP6Uv--vKt4wOZOWTKKtOhEKLQYclOq5fY12dY
設置 https 的連線
修改 virtual.conf 在後面加上
server {
listen 443 ssl;
listen [::]:443 ssl;
http2 on;
server_name your.domain.com
ssl_certificate /etc/nginx/ssl/live/n.sfs.tw/fullchain.pem;
ssl_certificate_key /etc/nginx/ssl/live/n.sfs.tw/privkey.pem;
location / {
proxy_pass http://somewhere.doamin.name:80/;
# or
root /path/to/your/site;
}
}
重啟 nginx 生效。
用瀏覽器查看憑證
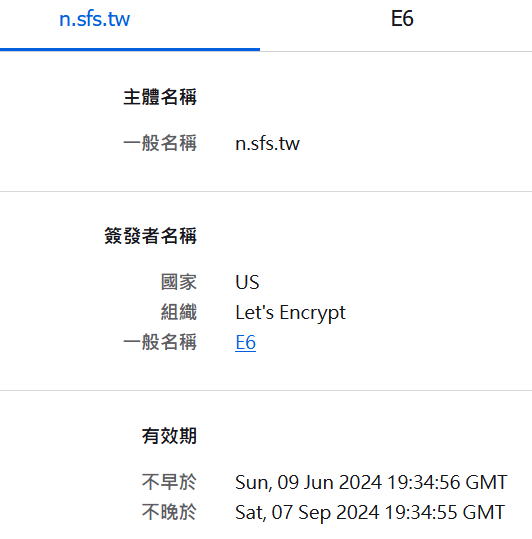
lets的憑證一次三個月,得手動或自動更新
自動更新 CERTBOT
手動更新
# docker compose run --rm certbot renew
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Processing /etc/letsencrypt/renewal/n.sfs.tw.conf
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Certificate not yet due for renewal- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
The following certificates are not due for renewal yet:
/etc/letsencrypt/live/your.domain.name/fullchain.pem expires on 2024-09-08 (skipped)
No renewals were attempted.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
排程更新
crontab -e
* * * */2 * /usr/bin/docker compose -f /home/docker/docker-compose.yml run --rm certbot renew
參考資料
[1] https://phoenixnap.com/kb/letsencrypt-docker
[2] 攻略docker版Let's Encrypt憑證申請 https://www.ccc.tc/article/letsencrypt
